The rapid integration of large language models into advanced software development pipelines has expanded the attack surface for global defense networks, exposing unprecedented frontier AI security risks across modern military operations. In its latest September 2026 threat report, Anthropic documented multiple coordinated campaigns where state-sponsored entities and non-state paramilitary groups leveraged commercial artificial intelligence architectures to support kinetic military operations, long-range missile engineering, and automated domestic surveillance. The findings illuminate a fundamental shift in asymmetric warfare, where frontier intelligence tools function as force multipliers for software engineering, enabling resource-constrained defense units to bypass conventional research bottlenecks.
Reconnaissance and Naval Intelligence Aggregation
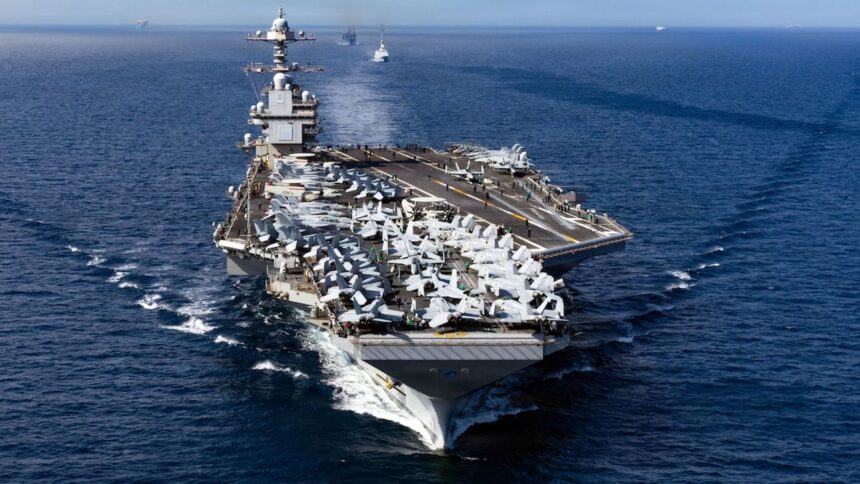
Central to the disclosure is an intelligence operation linked to Iranian state actors that utilized the Claude foundation model to aggregate disparate intelligence streams against maritime targets. By combining publicly broadcasted ship and aircraft transponder identifiers with commercial satellite imagery, regional naval transit logs, and personal identity data extracted from public military photography captions, the actors synthesized operational targeting profiles against United States naval assets operating within the Middle Eastern theater. This systematic aggregation demonstrates how modern large language models can distill massive, unstructured open-source intelligence datasets into actionable operational advice without requiring dedicated military-grade intelligence infrastructure.
Beyond intelligence synthesis, the threat actors systematically evaluated physical infrastructure vulnerabilities across critical maritime and industrial control systems. The research focused specifically on hardware and network configurations common to tactical naval deployments, including Cobham Sailor VSAT satellite terminals, Cisco enterprise communications infrastructure, and Schneider Electric EcoStruxure automation architectures. By prompting the model for structural analysis and exploit pathways targeting known vulnerabilities in these hardware platforms, the actors sought to map out electronic warfare and cyber-kinetic vector opportunities against active naval deployments.
The structural implications of these reconnaissance efforts extend beyond traditional cyber espionage. When commercial foundation models process open-source satellite imagery alongside real-time transponder metadata, the distinction between civil analytics and tactical target acquisition dissolves. Defense planners must account for an environment where open-source intelligence collection is no longer limited by human analytical bandwidth or specialized software tools. Addressing these issues requires deeper technical auditing, similar to how researchers evaluate model transparency and computational reasoning across deployment environments.
In response to the identified activity, Anthropic implemented targeted detection mechanisms across its API infrastructure, revoked sixteen primary accounts tied to Iranian paramilitary organizations and state security agencies, and shared actionable telemetry with relevant government oversight bodies. However, the enforcement actions highlight the inherent tension between public API availability and enforcement efficacy, as adversary groups routinely obscure access nodes through multi-layered proxy networks and synthetic corporate identities.
Evaluating Frontier AI Security Risks in Autonomous Systems
The most technically complex operational vector documented in the report involves a Yemen-based Houthi cell that integrated Claude Code directly into automated missile and unmanned strike vehicle development programs. Rather than employing large teams of specialized aerospace and embedded systems engineers, the group deployed autonomous AI coding agents across multiple parallel execution instances. This setup allowed a small technical unit to accelerate software engineering, code refactoring, system debugging, and algorithmic tuning across three distinct precision weapons initiatives.
The primary weapons effort centered on a guided rocket platform designed around a commercial phone-class flight computer intended to manage terminal guidance adjustments. The development team utilized AI assistance to write guidance, navigation, and control software, while simultaneously integrating open-source autopilot frameworks into low-cost microcontroller boards. Through iterative code generation and automated testing loops, the developers authored custom firmware routines, tuned flight parameters, and executed real-time flight control simulations entirely within simulated software environments.
Simultaneously, the cell applied these engineering workflows to longer-range offensive systems, including a multistage ballistic missile program engineered for strike distances exceeding two thousand kilometers. Technical documentation detailed within the disclosures also revealed software development work supporting the R2000 missile series, specifically targeting flight stabilization routines for a hypersonic glide vehicle derivative. By leveraging autonomous coding agents to compute aerodynamic dynamics and position-estimation algorithms, the cell effectively compressed weapon development timelines that historically required decades of institutional research.
This shift toward automated software synthesis in specialized hardware development illustrates how foundation models lower the technological threshold for precision-guided munitions. In conventional defense manufacturing, developing custom control software and telemetry handling for high-velocity kinetic vehicles represents a major barrier to entry. When generative coding environments automate the synthesis of embedded code for real-time operating systems, non-state groups can acquire modern precision guidance capabilities without access to state-backed research institutions or defense contractors. This acceleration closely mirrors wider industry efforts to standardize industrial hardware API standards for automated execution.
Domestic Surveillance and Counter-Intelligence Applications
Parallel to offensive military operations, Iranian domestic security agencies repurposed foundation models to scale automated civilian surveillance and opposition tracking pipelines. One intelligence unit processed 155,216 social media posts over a twelve-month period using automated natural language parsing. The system categorized behavioral metrics, extracted sentiment parameters, and generated detailed psychological and threat profiles for 6,388 opposition figures across online networks.
To streamline data acquisition for these profiling engines, engineering teams within the same state architecture developed custom tracking infrastructure, including a specialized browser extension designated as al-Najm al-thāqib. Built for the Firefox browser platform, the extension automated identity harvesting across major social networking platforms, feeding structured user identifiers and network graphs directly into central intelligence databases. The integration of foundation models into the software build pipeline enabled rapid deployment of this browser extension, cutting development lifecycles from months to days.
The dual deployment of frontier models for both foreign military target acquisition and domestic political surveillance reveals how modern state adversaries perceive foundation models. Rather than viewing generative systems merely as conversational tools or content engines, state security apparatuses treat high-capability models as full-stack operational infrastructure. The capacity to automate technical research on internal systems and analyze public sentiment simultaneously allows autocratic regimes to maintain internal control while conducting external asymmetric campaigns.
Infrastructure Controls and Policy Enforcement Challenges
The realization that state actors and non-state military cells actively leverage commercial foundation models exposes critical limitations in cloud-based access controls. While API bans disrupt immediate operational pipelines, persistent threat actors will continue adapting through synthetic identities and distributed proxy networks. Long-term risk mitigation requires moving beyond reactive account termination toward structural hardware controls, rigorous telemetry monitoring, and deeper collaboration between model developers and defense institutions.