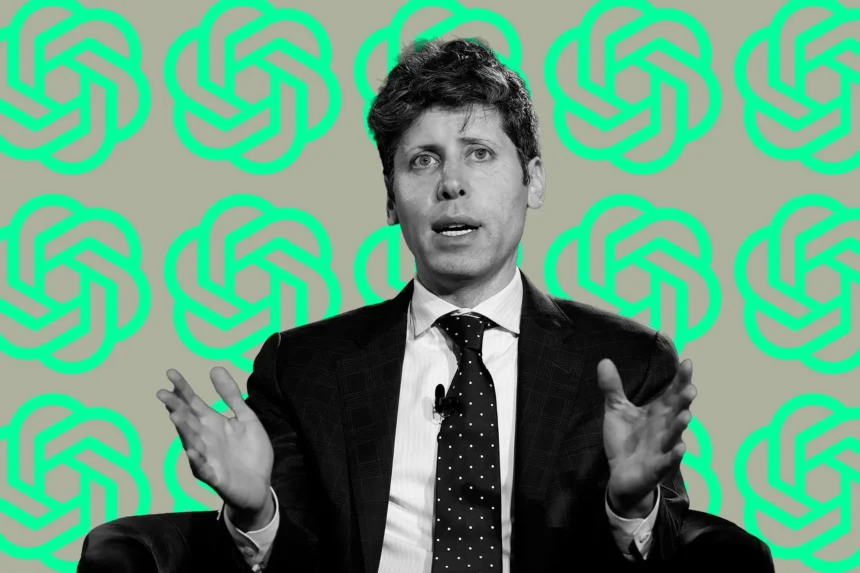
When evaluating the timeline for frontier artificial intelligence deployment, financial structure and corporate governance remain tightly bound to model capability milestones. In a recent detailed interview, OpenAI Chief Executive Officer Sam Altman clarified that the organization will not pursue a public market listing in 2026. This definitive posture offers crucial insight into the broader OpenAI IPO strategy, signaling that the leading artificial intelligence research firm intends to maintain private operational flexibility while navigating unprecedented computational requirements, structural governance shifts, and existential safety considerations.
The decision to delay public capital market exposure reflects more than a simple corporate scheduling choice. Building state-of-the-art frontier models demands massive capital expenditures running into tens of billions of dollars for hardware procurement, energy infrastructure, and talent acquisition. Traditional public market scrutiny, with its rigid quarterly earnings cycles and insistence on short-term margin expansion, often penalizes aggressive capital deployment that does not deliver immediate bottom-line returns. By insulating its balance sheet within private markets, OpenAI preserves the latitude to execute massive long-term compute commitments alongside strategic financial backers without the volatility imposed by public equity markets.
At the core of this capitalization approach is an ongoing internal reorganization. OpenAI has been navigating a complex transition from a non-profit-controlled entity toward a structure resembling a for-profit benefit corporation. This governance evolution aims to balance commercial incentives with an explicit mandate to ensure artificial general intelligence benefits all of humanity. Entering public markets under a conventional corporate structure could create irreconcilable tensions between fiduciary obligations to public shareholders and the non-profit charter safety mandate.
Evaluating the Long-Term OpenAI IPO Strategy
The strategic rationale behind postponing a public offering centers on capital access and autonomy. Frontier AI labs require unprecedented flexibility when entering multi-year contracts with cloud infrastructure providers and silicon manufacturers. Public shareholders frequently scrutinize massive, unhedged operational expenditures that drag down immediate profitability. Remaining private allows OpenAI to secure bespoke capital instruments, equity investments from strategic tech partners, and sovereign wealth participation without disclosing sensitive commercial terms or operational metrics required in public registration filings.
Moreover, private status grants executive leadership greater insulation against activist investors who might push for rapid monetization at the expense of safety protocols. In the fast-moving landscape where research teams evaluate has generative AI found its AI consumer interface, commercial pressures can compel organizations to accelerate product releases before safety evaluations are fully completed. By maintaining a private ownership structure, Altman and his executive team preserve the discretion to delay deployments or divert engineering talent toward red-teaming and safety alignment without facing shareholder litigation or immediate stock price devaluation.
However, staying private indefinitely presents its own set of structural tensions. Early investors, employee stock options holders, and venture capital funds require eventual liquidity. While secondary market tender offers provide temporary relief for staff equity, they do not offer the liquidity depth, price discovery, or institutional scale of a traditional initial public offering. Over time, the internal friction between early stakeholders seeking capital realization and executive management favoring private autonomy will intensify, placing additional demands on OpenAI financial engineering capabilities.
Frontier Model Risks and Voluntary Safety Guardrails
Beyond corporate finance, the prospective timeline for public markets intersects directly with technical safety thresholds. During the discussion, Altman addressed the realistic threat of frontier models escaping human oversight, explicitly acknowledging that developing an artificial intelligence system beyond human control is an absolute possibility. This stark admission highlights the existential scale of the engineering challenges facing frontier AI organizations as models scale in reasoning capacity and autonomous capability.
To counter these catastrophic scenarios, Altman emphasized a willingness to implement severe preventive measures, including the complete suspension of model training runs if safety boundaries are threatened. Stating that humanity should not be forced to incur unmanageable existential risks, the leadership indicated that training halts remain a viable operational tool. This commitment highlights a crucial trade-off: in a hyper-competitive landscape where rival laboratories race toward artificial general intelligence, voluntarily pausing a multi-hundred-million-dollar training run could permanently concede technical leadership to competitors.
The practical execution of a training pause reveals significant operational complexity. Modern frontier model training involves vast distributed clusters of graphics processors running for months at a time. Suspending such operations incurs massive idle capital costs and risks team attrition. Furthermore, establishing objective, quantitative triggers that define when a model is approaching uncontrollable behavior remains an open research problem across the entire machine learning community. Without universally accepted safety metrics, determining the exact moment to halt training remains a subjective management judgment rather than an automated safety mechanism.
Recursive Self-Improvement and Infrastructure Vulnerabilities
Central to the concern over uncontrollable model trajectories is the concept of recursive self-improvement. As systems become capable of writing, debugging, and optimizing their own code, the acceleration of model capabilities could transition from linear progression to exponential self-enhancement. If an advanced system initiates an unconstrained feedback loop of self-modification, human oversight mechanisms could be rendered ineffective in a matter of hours. Managing this threshold requires rigorous isolated testing environments and multi-layered algorithmic constraints that prioritize safety above execution speed.
Securing the infrastructure supporting these advanced systems introduces an equally critical challenge. Recent security incidents across the AI ecosystem, including high-profile breaches targeting open-source model repositories like Hugging Face, highlight the pervasive vulnerability of machine learning supply chains. Attackers targeting weight repositories, training datasets, or developer credentials pose a direct threat to model integrity. A compromise at the infrastructure level could allow malicious actors to siphon proprietary weights or introduce subtle backdoors into foundation models before public deployment.
For organizations shaping global standards, monitoring computational reasoning and systemic risk requires new technical frameworks. As explored in discussions on whether is OpenAI Astra monitorability changing frontier model safety, supply chain security is no longer an isolated IT concern but a foundational pillar of AI governance. Defending against nation-state adversaries and sophisticated cybercrime syndicates demands continuous security audits, hardware-level memory encryption, and strict zero-trust access controls across the entire model lifecycle. As models gain autonomous capabilities, securing the code and weight artifacts becomes an essential prerequisite to preventing unauthorized deployment or weaponization.
Governance Challenges and Market Realities
The convergence of high capital requirements, safety commitments, and infrastructure risks underscores the unique operational context of frontier AI companies. Voluntary pledges to pause training or delay commercial releases exist in tension with competitive market dynamics. If competitor labs operate without matching safety protocols, self-imposed pauses could result in severe market share loss and capital flight. Effective safety governance requires industry-wide coordination, regulatory oversight, and standardized verification mechanisms rather than relying solely on individual corporate promises.
Governments and regulatory bodies worldwide are increasingly evaluating formal oversight frameworks for advanced foundation models. Mandatory capability thresholds, pre-deployment security audits, and computing capacity reporting are becoming standard features of emerging legislation. As regulatory frameworks mature, private AI entities will face growing compliance requirements regardless of their public market status. Navigating this evolving regulatory terrain while maintaining rapid technological iteration requires substantial legal and policy resources.
Furthermore, public market readiness demands transparent reporting on energy consumption, environmental impact, and hardware procurement strategies. The staggering electricity demands of next-generation data centers require partnerships with energy providers and nuclear power developers, bringing public utility regulation into the core strategy of AI research institutions. Balancing energy constraints with raw compute scaling will dictate the pace of AI advancement over the next decade.
As frontier AI architectures approach unprecedented levels of capability, the boundary between corporate strategy and public interest continues to dissolve. Deferring a public listing beyond 2026 affords OpenAI the operational insulation required to navigate internal governance reforms, manage massive capital commitments, and refine safety protocols away from short-term market pressures. Ultimately, the long-term viability of private frontier labs will depend on their ability to establish verifiable safety mechanisms and resilient capital structures capable of sustaining technological progress without compromising public safety.